
Vulnerability
SonicWall urges immediate patching of chained vulnerabilities
Two chained vulnerabilities (CVE-2026-83548 and CVE-2026-83549) have been disclosed in SonicWall SMA1000 series appliances, potentially leading to remote code execution. The former is a server-side request forgery vulnerability with a severity score of 10, while the latter is an OS command injection vulnerability with a score of 7.8. SonicWall has confirmed exploitation in the wild, and CISA has added them to its Known Exploited Vulnerabilities catalog, mandating federal agencies to remediate by Saturday.
Frontier AI helps exploit flaws in tests using key industrial devices
A Forescout Research - Vedere Labs report indicates that frontier AI can be used to exploit vulnerabilities in programmable logic controllers (PLCs), devices recently targeted by hackers, affecting U.S. water, energy, and factory operations. Researchers used Claude to port a remote code execution vulnerability in WAGO PLCs to another model, but the AI still required human guidance.
CISA identifies security hurdles that led to very different results in two red-team engagements
In a report released Tuesday, CISA detailed the differing outcomes of two red team exercises. One organization (A) failed to stop the attack due to a lack of communication between security operations centers (SOCs) and being overwhelmed by false-positive alerts; the other (B) limited the attack's spread through rapid response and a mature security posture, but still exposed vulnerabilities in cloud identity management. The report summarized six common shortcomings, including insufficient alert tuning, excessive permissions, and credentials that never expire.
AI-backed campaign targeting vulnerable Siemens S7 devices, CISA and FBI warn
The FBI, NSA and CISA issued a joint advisory on Wednesday regarding an AI-assisted campaign targeting Internet-exposed Siemens S7 programmable logic controllers (PLCs). Attackers are using AI-generated scripts disguised as monitoring software to gain access, steal credentials and disrupt industrial processes. The advisory covers S7-200 through S7-1500 series models and follows recent Iran-linked attacks on water utilities.
GitLab issues emergency patch for critical code-injection flaw
GitLab 于周一发布带外安全补丁,修复一个被追踪为 CVE-2026-19478 的严重代码注入漏洞,该漏洞可允许未认证攻击者通过 GraphQL 指令远程修改或删除公共项目及用户数据,CVSS 评分为 9.4。威胁情报公司 watchTowr 在公开披露后数分钟内即复现漏洞,并确认已出现野外利用。
Critical flaw in SAP Commerce Cloud faces initial exploitation attempts
Security researchers have detected early exploitation attempts against a critical vulnerability in SAP Commerce Cloud, tracked as CVE-2026-58231, only three days after SAP issued a patch. The flaw, which carries a maximum severity score of 10, involves abuse of a default authentication client and could lead to arbitrary code execution. While activity appears limited to a single threat actor, experts warn of the high risk due to the ease of exploitation and the sensitive data at stake.
Cisco says software vulnerability could let hackers crash firewalls
Cisco is alerting customers to a high-severity vulnerability in its Secure Firewall ASA and FTD software. Tracked as CVE-2026-20349, the flaw could allow remote attackers to crash devices via malformed HTTP requests. Cisco has released fixes, and CISA has added the bug to its Known Exploited Vulnerabilities catalog, giving federal agencies until Aug. 14 to patch.
Secure development can help turn the tables as AI alters cyber landscape
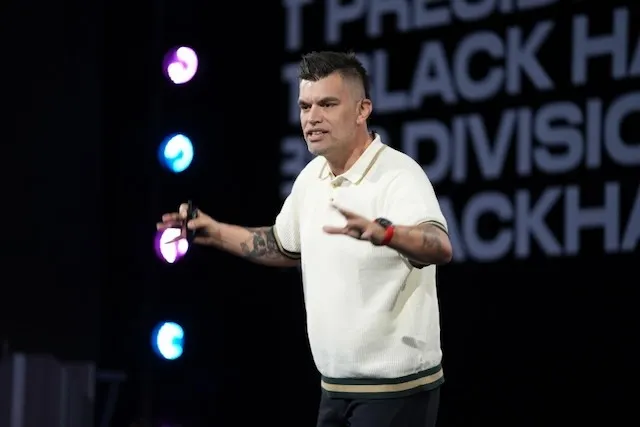
In his keynote at Black Hat USA, Microsoft's Vice President of AI Security, David Weston, stated that AI is enabling attackers to discover and weaponize software vulnerabilities at unprecedented speed, making traditional patch management insufficient. He called on the industry to pivot to secure development practices, proactively building safer software to reverse the offensive-defensive dynamic.
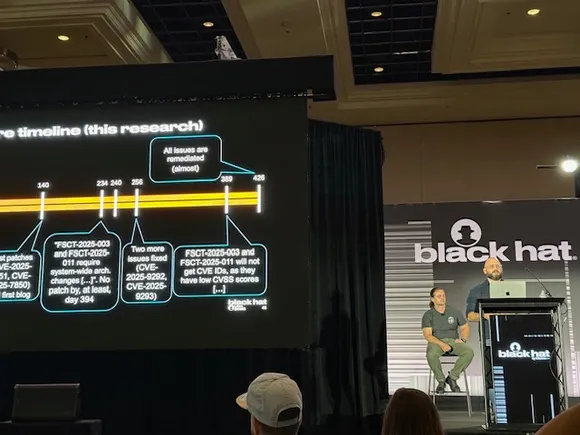
Critical flaws allow hackers to exploit zero-touch provisioning process in TP-Link Omada
Researchers discovered 15 new vulnerabilities in TP-Link Omada's zero-touch deployment process, which can be chained by hackers to gain initial access and move laterally. The vulnerabilities affect devices such as routers, firewalls, and IP cameras. TP-Link has released security advisories and patches.
Hackers grow more willing to destroy, not just disrupt, OT systems
At Black Hat USA 2025, security experts noted that cyberattacks on operational technology (OT) systems are shifting from data theft and ransomware to physical destruction, with Iran-linked hackers demonstrating the ability to disable safety monitoring systems. Due to numerous industrial devices having default passwords, unpatched vulnerabilities, and lacking encryption protection, attackers can cause severe damage without advanced AI or zero-day exploits.