
Strategy
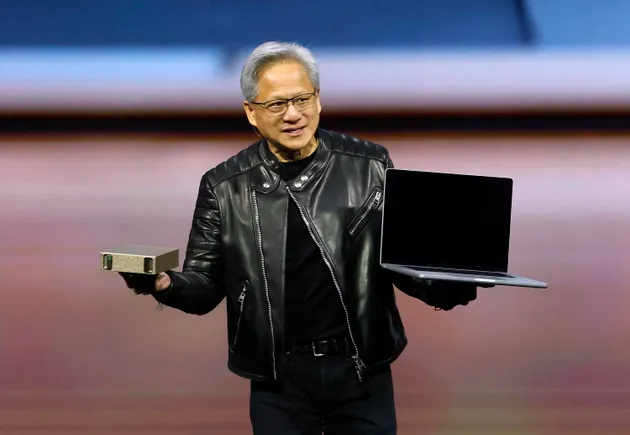
Nvidia’s $12.9B Hugging Face deal could benefit enterprises
Nvidia confirms the acquisition of open-source AI platform Hugging Face for $12.9 billion, marking its second-largest deal after acquiring Groq assets. The move aims to expand the developer community and strengthen its presence in the AI operating system space. Analysts note that the deal may bring more security resources to Hugging Face, enhancing the reliability and model evaluation capabilities that enterprise CIOs rely on, but it will have little impact on enterprise costs in the short term, with long-term attention needed on changes in bargaining power.
Security policies fail to keep up with a hybrid cloud world
A report released by the Cloud Security Alliance in August points out that misconfigured security policies are causing issues such as application outages and audit failures. The survey shows that about two-thirds of enterprises have experienced outages of business-critical applications due to security policy misconfigurations in the past 12 months, and 92% of respondents said they find it difficult to fully grasp security policies in cloud environments. The report recommends that enterprises achieve unified visibility, automate policy changes, and continuously assess compliance.
Cisco security revenue jumps 14% as agentic AI sharpens cyberattacks
Cisco's fiscal Q4 2026 results show security revenue up 14% to $2.2 billion, with total revenue at $17.3 billion. CEO Chuck Robbins attributes growth to agentic AI expanding the threat landscape, while industry data from IBM and Incode highlight rising AI-enabled attacks and fraud.
Researchers find AI-powered hacking tools for sale in underground forums
A new report from Trellix reveals a marketplace for AI-driven hacking tools on underground forums, including attack planning services, evasion tools, and unrestricted AI models. The findings highlight how AI is commoditizing advanced threat capabilities.
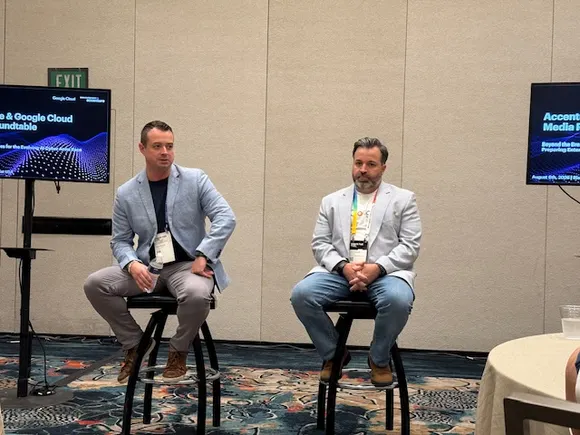
AI Models Exploited by Hackers to Uncover Novel Attack Vectors
At Black Hat USA 2025, researchers from Accenture and Google Cloud revealed that threat actors are increasingly abusing AI models—especially open-weight variants—to discover new entry paths into corporate IT networks. These groups leverage AI for exploit development, faster attacks, and persistence via legitimate tools. The shift toward open-weight models allows circumvention of guardrails on frontier AI, lowering entry barriers. Recent incidents, including an OpenAI agent breaching Hugging Face, underscore the growing AI security arms race.
AI is widely used to exploit critical vulnerabilities and disrupt supply chains
A report released by CrowdStrike on Monday noted that malicious use of AI has rapidly accelerated, with some threat groups embedding AI in their cyber operations. China-linked groups Vault Panda and Genesis Panda used AI to exploit critical vulnerabilities within 24 hours of proof-of-concept disclosure; North Korea-linked group Stardust Chollima injected malicious npm packages into 131 trusted Mastra AI frameworks through supply chain attacks. CrowdStrike's head of counter-adversary operations, Adam Meyers, warned that the vulnerability exploitation window has shortened to hours, with zero-day vulnerability weaponization outpacing traditional patch cycles.
OT Security Alliance Calls on Congress and CISA to Advance Reforms in Response to Cyberattacks on Water Sector
U.S. water facilities were attacked by hackers suspected of being linked to Iran, affecting at least seven states. The OT Cybersecurity Alliance calls on CISA to issue binding operational directives and asks Congress to take three specific measures to strengthen critical infrastructure security.
Chinese-speaking attacker leverages DeepSeek for autonomous threat operations
A Unit 42 report reveals that a Chinese-speaking attacker used DeepSeek and the Hermes Agent framework for autonomous cyberattacks, scanning GitHub for popular PoCs and attempting to exploit vulnerabilities in Langflow, n8n, and others, but most attacks failed due to authentication requirements, with only manual exploitation of Citrix NetScaler and Marimo vulnerabilities succeeding.
The Implications and Limitations of the Trojan Horse Metaphor for AI Safety
The Trojan horse story is often used as a metaphor for AI safety risks, but this article argues that Agentic AI does not create a new category of risk, but rather amplifies existing patterns of exploiting trust in supply chain attacks. Drawing on discussions from Cympire and Forbes, the article compares traditional Trojans with AI agents, proposing a return to third-party risk management frameworks, centering on 'permissions' rather than 'access,' and using four key questions to construct a governance strategy.
The Mythos Era: Security Defenses Must Move Forward to Runtime
In security history, defenders once relied on a time gap—averaging two and a half years from vulnerability disclosure to weaponized exploitation, but by 2026 this has shrunk to hours, with the frontier model Mythos as the primary cause. This brings a dual challenge: unknown attacks (zero-day vulnerabilities with no CVE to look up) and a flood of known vulnerabilities (report overload causing prioritization chaos). Static code scanning cannot solve either problem; only runtime execution-based monitoring, which observes code and agent behavior in real time, can block unknown threats without relying on CVEs and filter out truly exploitable vulnerabilities, turning prioritization from guesswork into precision.