
Deep Dive
来自我们记者的行业洞察
Software and AI Companies Form Alliance to Combat Open Source Software Security Vulnerabilities
Several technology companies, including Anthropic, AWS, IBM, and Microsoft, announced a joint effort to discover, disclose, and fix security vulnerabilities in open source software. The alliance, named Akrites, will establish a shared security incident response team and a coordinated vulnerability disclosure process. This initiative is primarily driven by the emergence of frontier AI models, which have greatly accelerated the speed of vulnerability discovery, while the existing open source ecosystem struggles to respond quickly.
Cybersecurity Dive Trendline on Vulnerability Management
The Trump administration announced the launch of a vulnerability management hub called Gold Eagle, aimed at coordinating the security community to use cutting-edge AI models to quickly identify and fix vulnerabilities. The project, led by the White House, operates the VINCE platform in partnership with Carnegie Mellon University's Software Engineering Institute, focusing on open-source software to address the pressure on the security community from the AI-driven surge in vulnerabilities.
Researchers warn about chained SharePoint sequence
Researchers at VulnCheck warn that two critical Microsoft SharePoint vulnerabilities—an authentication bypass (CVE-2026-55040) and an input validation flaw (CVE-2026-63520)—can be chained to let unauthenticated attackers execute code on vulnerable servers. While the auth bypass alone has limited impact, chaining it with the second flaw achieves full criticality. Rapid7 disclosed a proof of concept on Aug. 11; exploitation was confirmed days later. Microsoft has released patches in its July and August security updates. Defused researchers report probing activity against honeypots using the chain.
CISA orders agencies to fix exploited Zimbra vulnerability
CISA added the Zimbra vulnerability (CVE-2026-73570) to its Known Exploited Vulnerabilities catalog, requiring federal agencies to complete patching within three days. The vulnerability has been exploited by hackers since mid-August, and thousands of organizations worldwide still use vulnerable versions.
UK power facility disabled for days after suspected state-linked cyberattack
UK government officials confirmed that a small power facility was forced to shut down for four days in July due to a suspected cyberattack linked to Iran. Officials stated the incident affected only a single facility and did not have a broader impact on the national power grid.
House Democrats ask GAO to study CISA workforce cuts
Several senior House Democrats sent a letter to the Government Accountability Office (GAO) requesting a study on the recovery of the Cybersecurity and Infrastructure Security Agency (CISA) following large-scale layoffs and mission adjustments, assessing the impact on critical infrastructure protection and cyber threat response capabilities.
Microsoft discloses maximum severity flaw in Entra ID
Microsoft disclosed a critical remote code execution vulnerability in Entra ID, identified as CVE-2026-69836, with a severity score of 10 out of 10. The vulnerability is related to the deserialization of untrusted data and was discovered by Microsoft's own security researchers. Microsoft stated that the vulnerability has been fully mitigated, requiring no additional action from customers, and emphasized that the disclosure aims to enhance transparency.
AI-powered vulnerability clearinghouse faces deep skepticism, major challenges
One month after launch, the U.S. government's AI-enhanced Gold Eagle vulnerability clearinghouse faces skepticism from cybersecurity experts over its limited scale, voluntary participation, Treasury Department leadership, and unclear integration with private-sector coordination hubs. While some see potential value in patch awareness and prioritization, concerns persist about funding, centralization risks, and the need for realistic scope.
CVE Program eyes automation and globalization to weather AI ‘vulnpocalypse’
At Black Hat USA and DEF CON 2026, CVE Program leaders acknowledged the unprecedented surge in AI-generated vulnerability reports but expressed confidence in the program's scalability. They discussed automation in triage, pilot CNA status for OpenAI and Anthropic, and the importance of prioritization and global alignment, while addressing concerns about the program's future after the 2025 funding crisis.
How volunteer cyber experts are helping protect rural water systems
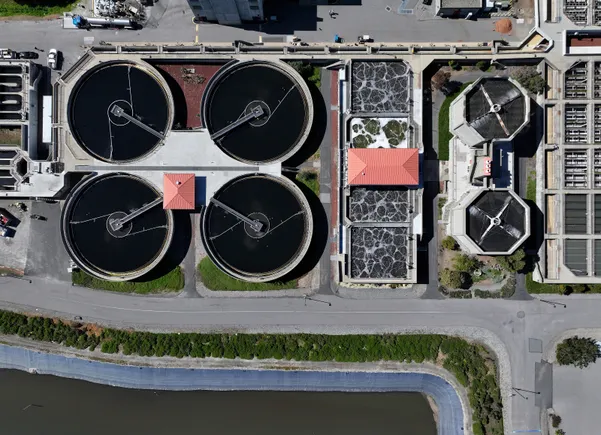
Since its launch in late 2024, the DEF CON Franklin Project has dispatched 27 volunteers to 21 water facilities, providing diverse support ranging from basic password management to emergency response planning. The project has not only enhanced the defensive capabilities of participating facilities but also, through research, uncovered real-world issues such as free security services coming with 'strings attached' and staffing shortages at small facilities. Despite its limited scale, the project's experience is spreading among peers through word of mouth.