
Deep Dive
来自我们记者的行业洞察
Healthcare Cybersecurity Alert: 385M Patient Records Exposed, Experts Urge Stronger Defenses
The healthcare industry faces increased cyberattack risks due to the widespread adoption of electronic records and digital services. Federal data shows that 385 million patient records have been exposed from 2010 to 2022. Experts urge organizations to strengthen security and call on regulators to raise standards.
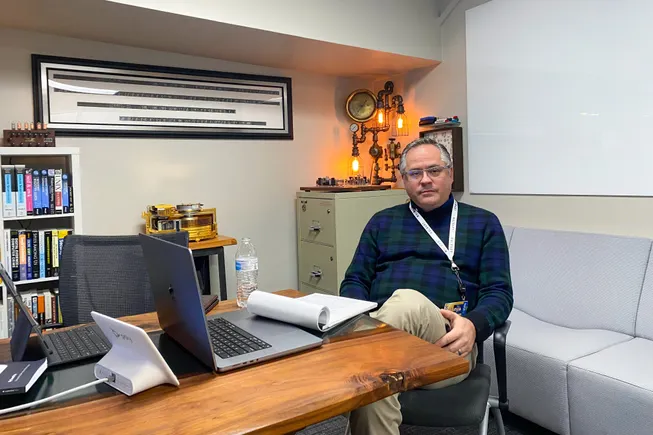
Inside Walmart's Security Operations Frontline: Scale, Trust, and Defense Strategies
In Bentonville, Walmart's headquarters, a carefully orchestrated conversation lifted the veil on its security operations. From a security operations center processing six trillion data points daily, to a forensics laboratory equipped with cleanrooms and X-ray technology, to a defense system blocking 8.5 billion malicious bots monthly, Walmart is fulfilling its commitment to 'becoming the world's most trusted retailer' with rare scale and institutional investment. Based on on-site visits and interviews with multiple executives, this article analyzes the uniqueness of its security strategy.
Where Does AWS Stand in the Cybersecurity Conversation?
AWS dominates the cloud market, but its voice in the cybersecurity community is not as prominent as that of Microsoft and Google. Although AWS is not inferior in security capabilities, its shared responsibility model and customer-centric approach to information disclosure make it appear conservative in security thought leadership. Multiple analysts point out that this low-key stance may stem from business strategy rather than insufficient security investment.
After the CommonSpirit ransomware attack: Why healthcare M&A has become a 'huge' cybersecurity risk
CommonSpirit Health suffered a ransomware attack this month, drawing attention to cybersecurity risks during the integration period of healthcare industry mergers and acquisitions. Experts point out that system integration, weak supply chains, and distracted executive attention during M&A make healthcare organizations more vulnerable to attacks. The FBI has also warned that ransomware groups tend to launch attacks during major financial events.
Medical Device Software Bill of Materials Reaches a Turning Point: Peering Under the Hood at Security Challenges
The software bill of materials (SBOM), as a tool to enhance cybersecurity in medical devices, has entered a critical development phase driven by the Biden executive order and NTIA initiatives. The FDA plans to incorporate SBOM into premarket submission requirements and is exploring a broader cybersecurity bill of materials (CBOM). However, the industry has concerns about information leakage risks and implementation burdens, with NTIA and AdvaMed debating access control and standardization.
Microsoft Repositions Itself Amid Threat Attacks, Pushes Image as Guardian of Cybersecurity
The COVID-19 pandemic brought Microsoft a 34% increase in commercial cloud revenue, but incidents like SolarWinds also put its security capabilities to the test. By integrating products, acquiring companies such as Rubrik, investing $20 billion to bolster security, and appointing Charlie Bell to lead a new security division, Microsoft aims to solidify its position as a provider of end-to-end security solutions in the era of remote work.
Aging Medical Devices and Growing Cyber Threats: A 'Perfect Storm' in Healthcare Cybersecurity Is Brewing
As ransomware attacks become increasingly sophisticated, one of the biggest cybersecurity challenges for healthcare organizations is defending aging medical devices against emerging cyber threats. These devices were often designed without cybersecurity in mind and run on operating systems that have reached end-of-life, making them difficult to patch.
Four Types of Technical Tools Help COVID-19 Vaccine Supply Chains Guard Against Fraud, Counterfeiting, and Cyberattacks
Moderna, Pfizer, and Johnson & Johnson vaccines have received FDA emergency use authorization, and AstraZeneca also plans to submit for review. The global distribution of multiple vaccines across multiple supply chains brings unprecedented complexity, also fostering cyberattack and counterfeiting risks targeting vaccine research and distribution. Industry experts point out that zero trust strategies, real-time visibility tracking, distributed ledgers, and digital authentication and serialization are four key technical tools for current risk prevention.